Defence Lab
what we protect
PeopleCode & deliveryInfrastructure & cloudDevicesOfficesGovernance & compliance
services
DevShieldSOCvCISOPenetration testingISO 27001 & SOC 2 readinessCompliance readinessSecurity health checkSecurity posture assessmentDevSecOpsThird-party riskDORA readinessCRA readinessAll 18 services
products
PhishAttackSecurity TrainingPhish GuardOffice Audit PortalMacBook AuditManaged Security Gate vendors blog about us book a consultation

PhishAttack

Test your exposure to MFA-bypass phishing — then turn results into training

Fully self-hosted, authorized phishing simulation that runs real adversary-in-the-middle attacks, records what happens on the phishing page, and turns the result into a targeted training assignment — testing both how people respond and whether your login flow can be bypassed.
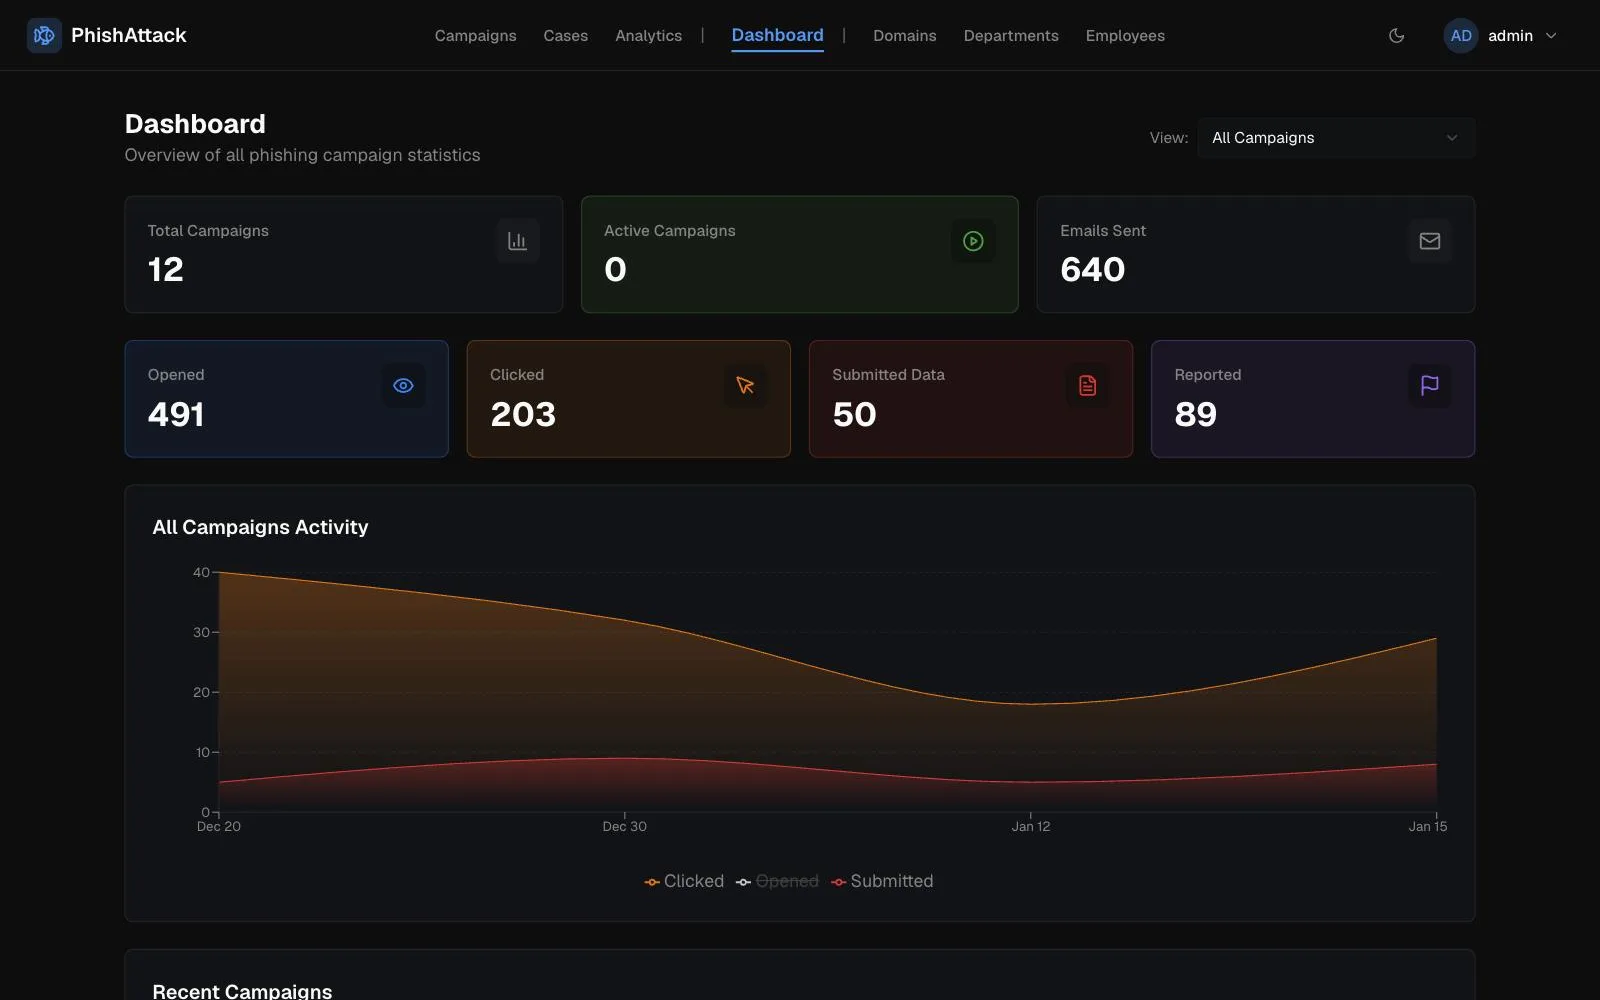
Dashboard

An authorized simulation — not an attack, not another awareness tool

It tests both how employees respond to phishing and whether your login flow resists an adversary-in-the-middle attempt, then assigns follow-up training on the result. Not a live attack, not a credential thief you aim at others, not a replacement for broad awareness training — it measures MFA-bypass exposure and closes the loop.

Dashboard
1 / 4

Dashboard

Why MFA is no longer the finish line

62% of breaches involve a person — the human layer, not the firewall, is where modern attacks land first (Verizon DBIR 2026).

Attackers walk straight past MFA — adversary-in-the-middle kits steal live session tokens, so a stolen second factor no longer stops them.

Awareness tools test 2015-era attacks — a typed password on a static fake page never proves whether your MFA can be bypassed.

The test and the fix are two products — by the time training happens the teachable moment is gone, and almost nothing changes.

The most powerful part, engineered as a safeguard

Authorized use only — written rules of engagement, scope defined up front.

Awareness Mode ON by default — captured credentials blocked, employee shown a teaching page.

Encryption at rest for tokens and credentials, with a retention and auto-destruction policy.

Self-hosted custody — you own the database; no employee behavior leaves your infrastructure.

Who it is built for, and who it is not

Built for

  • Regulated mid-market and enterprise CISOs who must own their behavioral data.
  • Pentest / red-team firms needing real AiTM hijacking plus recording as a client deliverable.
  • MSPs running multi-tenant, self-hosted campaigns across client orgs.

Not the fit (yet)

  • Teams wanting smishing, vishing or QR simulation — not supported yet.
  • Buyers who need a turnkey SaaS with no infrastructure to run.
  • Teams that only want standalone awareness training with no phishing simulation behind it.

A real clone of the real login, not a fake page

Evil Pages are Evilginx reverse-proxy clones of the actual login flow (Okta, Microsoft 365, Google). They capture the live session token and bypass 2FA/MFA — something a static fake page cannot test. 22 bundled phishlets, extensible via YAML config for any OAuth/SAML Service.

CapabilityPhishAttackAwareness training platformOpen-source campaign tool
Reverse-proxy Evil PagesYesNoNo
Real 2FA / session-token captureYesNoNo
Session recording / replayYesNoNo
Self-hosted, no per-seatYesNoYes
Training assigned from what was capturedYesPartialNo

From campaign to trained employee in one loop

  1. Build a campaign — templates, recipient groups, department targeting; delivery over SMTP or Gmail API insert.

  2. Schedule it — one-time or recurring, with Cohort Mode splitting recipients by percentage and scenario.

  3. Capture the session — the Evil Page proxies the real login and records the live token.

  4. Replay what happened — rrweb session recording tied to that recipient and campaign.

  5. Close the loop — the phish event auto-creates a targeted training assignment for that employee.

A flat cost, not a per-seat bill

No per-seat fees — a flat self-hosted cost instead of a subscription that grows with headcount.

Self-hosted license

Best for
In-house security teams owning their data
Value anchor
Flat infra + license, no per-seat

Final quote scoped per engagement.

Per-client instance

Best for
MSPs across many client orgs
Value anchor
Multi-tenant, unlimited internal re-use

Final quote scoped per engagement.

See it capture a real session token

Book a live demo and watch a real session-token capture, a session replay, and the phish-to-training auto-assignment run end to end — on a platform you would host yourself.

Book a live demo